
About the incident
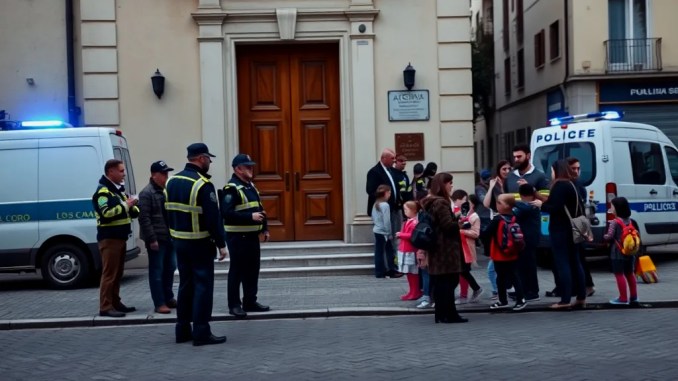
Italian authorities received mass email bomb threats sent to around 300 schools. Local police coordinated immediate evacuations, moved students to safe perimeters and began forensic tracing of the messages. School staff followed pre-existing emergency protocols to account for pupils and maintain calm while law enforcement conducted building searches.
Who sent the emails and what did they claim?
The emails carried a signature that referred to “Misojinistan Province leader Mikhail Andropov.” Investigators treat that identifying line as a lead, not conclusive evidence of origin. Cyber-forensics teams are analyzing message headers, sending IP addresses, mail-server logs and metadata to determine whether the emails were spoofed, routed through intermediary servers or originated from compromised accounts.
Immediate safety steps taken at schools
Authorities and school administrators enforce standard active-threat procedures: swift evacuation to predesignated assembly points, roll-call using class lists, triage for anyone needing medical attention, and cordoning buildings for police sweep teams. Teachers kept students together under supervision; parents received official updates through school messaging systems to prevent circulation of conflicting information.
How police investigate mass email threats
Investigators follow a step-by-step digital and physical workflow:
1) Preserve evidence: Secure original emails, mail server logs and devices used by recipients.
2) Trace technical metadata: Extract message headers, examine Received lines, and identify relay servers.
3) Cross-check signatures and claims: Compare textual elements and named signatures against known hoaxes and threat databases.
4) Coordinate with telecom and hosting providers: Request IP logs, subpoena records where necessary to identify senders.
5) On-site searches: Police conduct physical sweeps with explosive ordnance disposal (EOD) teams when a credible threat cannot be ruled out.
6) Forensic follow-up: If perpetrators are identified, prosecutors pursue charges for false threats, public endangerment or terrorism-related statutes as applicable.
What parents and school staff should do now
Parents should rely on official school channels for updates, avoid sharing unverified social posts and prepare to present identification and contact details should reunification protocols require it. School staff should preserve all communications, document actions taken during evacuations, and cooperate with investigators by providing logs and witness statements.
Potential motivations and profiling considerations
Mass hoax threats can aim to disrupt daily life, test response capabilities, create fear, or divert resources from other actions. Profiling motivations requires corroborating digital forensics with behavioral evidence—timing of emails, language patterns, geopolitical references and any past threats directed at the same institutions.
Examples and precedent
Similar mass-email hoaxes have targeted schools in several countries; In many cases senders used anonymizing services or hijacked third-party servers. In past incidents, coordinated international cooperation between police and hosting providers led to arrests when investigators traced back to slip-ups in operational security by perpetrators, such as reusing an account or leaving identifiable metadata.
Why quick, evidence-based communication matters
Clear, factual messages from schools and police reduce panic and limit dangerous behavior (like unsafe return attempts to buildings). Providing concise instructions—where to go, what to bring to reunification points, and when official all-clear will be issued—keeps families informed and supports orderly incident response.
What to expect next from investigators
Expect authorities to publish layered updates: an initial safety bulletin, then technical findings as investigations progress, and finally, when appropriate, legal actions or arrests. If emails are traced to foreign infrastructure, investigators will likely request international cooperation through mutual legal assistance treaties and contact hosting providers to preserve and analyze logs.
Practical checklist for schools to tighten resilience
Short-term: review and rehearse evacuation and reunification plans, test mass-alert systems, and ensure contact databases are current.
Medium-term: implement stronger email filtering, enable DMARC/DKIM/SPF records to reduce spoofing success, and train staff for rapid verification and controlled communication.
Long-term: invest in coordination drills with local police, run tabletop exercises for cyber-physical threat scenarios, and establish clear policies for post-incident counseling and community restoration.

Be the first to comment