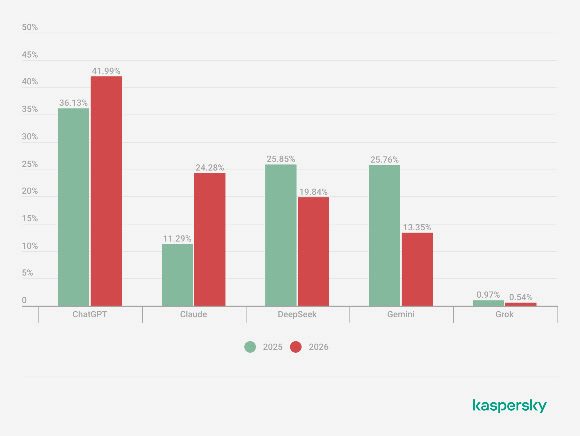
In an alarming trend, over 33,300 cyberattacks aimed at small and medium-sized businesses (SMBs) were detected between January and April 2026, representing a nearly fivefold increase compared to the same period in 2025. Many of these attacks exploit popular artificial intelligence (AI) services as malicious tools, disguising harmful software behind trusted AI platforms to trick users and infiltrate networks. Why are cybercriminals leveraging AI services? Simply put, AI platforms such as ChatGPT, Claude, and DeepSeek have become integral to daily workflows, making them prime targets for impersonation. These attackers craft malicious scripts and fake AI applications that mirror legitimate platforms, luring SMB employees into downloading or executing harmful files. In early 2026, ChatGPT was involved in 42% of these impersonation attacks, followed by Claude (24%) and DeepSeek (20%). Attackers often distribute Trojan horse malware or ransomware hidden within seemingly innocuous AI-like tools, which can silently infiltrate enterprise systems, stealing or destroying valuable data. Kaspersky researchers found that these malicious programs frequently take the form of Trojan variants designed to evade detection, camouflaging as regular files or applications. Once inside a device, they may deploy additional payloads, such as spyware, credential stealers, or backdoors, making it crucial for SMBs to recognize and respond promptly. The Rise of Malicious AI-Simulating Files Cybercriminals craft fake AI applications that mimic the appearance and functionality of genuine tools. These files often leverage social engineering tactics, urging users for immediate action, like “Update your AI plugin now” or “Download the latest AI toolkit.” Once downloaded, these files can execute malicious code, granting attackers persistent access to the network. Analyzing attack vectors reveals that Trojan horses are the most prevalent malware in these scenarios. They typically infiltrate via phishing emails, malicious links, or compromised websites designed to look like legitimate AI service providers. Once on the network, they establish backdoors, enabling persistent access and potential lateral movement across systems. Cybercriminals Exploit Popular Messaging and Video Apps Equally concerning is the surge in attacks that target instant messaging platforms like WhatsApp, Telegram, Zoom, and Microsoft Teams. Criminals embed malware into seemingly innocent messages, often using spoofed IDs or compromised contacts, to lure employees into clicking malicious links or downloading infected files. Kaspersky’s telemetry confirms that between January and April 2026, over 415,000 such malicious messages were blocked, indicating high volumes of ongoing attacks. These campaigns often leverage urgency and fear tactics, pressuring employees to respond quickly without proper scrutiny. Advanced Malware Techniques and Their Impact The malware employed in these scams exhibits advanced behaviors aimed at avoiding detection: – Code obfuscation to mask malicious intent. – Multi-layered payloads that activate only upon specific triggers. – Use of legitimate system processes to hide activity. – Integration with AI-based tools for dynamic decision-making, making detection more challenging. For example, malware may lie dormant until detecting specific user behaviors or network conditions, then activate to maximize impact. Protection Strategies for SMBs Given the sophistication of these threats, SMBs need to take proactive measures: 1. Implement comprehensive security solutions that include behavioral detection, sandboxing, and real-time monitoring—products like Kaspersky Small Office Security can provide layered defense. 2. Educate employees regularly about the risks of AI impersonation, phishing, and suspicious links. Regular security awareness training is vital. 3. Verify the authenticity of AI-related applications and plugins by confirming their official sources before installation. 4. Restrict access to AI tools to trusted personnel, and monitor recent downloads and activity logs. 5. Use multi-factor authentication (MFA) across all critical access points to prevent credential theft. 6. Maintain regular backups of essential data and ensure that restoration procedures are tested. 7. Deploy email and web filtering tools capable of identifying and blocking malicious content with AI-driven threat intelligence. Emerging Threats Require Vigilance The landscape is evolving rapidly, with attackers continuously refining their tactics to exploit the trust in AI and ubiquitous communication platforms. SMBs must stay informed and adapt their security posture accordingly. Threat intelligence experts emphasize that cybersecurity is a continuous process, not a one-time fix. By understanding the modus operandi of threat actors, embracing layered security measures, and fostering a culture of awareness, SMBs can significantly reduce their risk of falling prey to these high-impact cyberattacks.